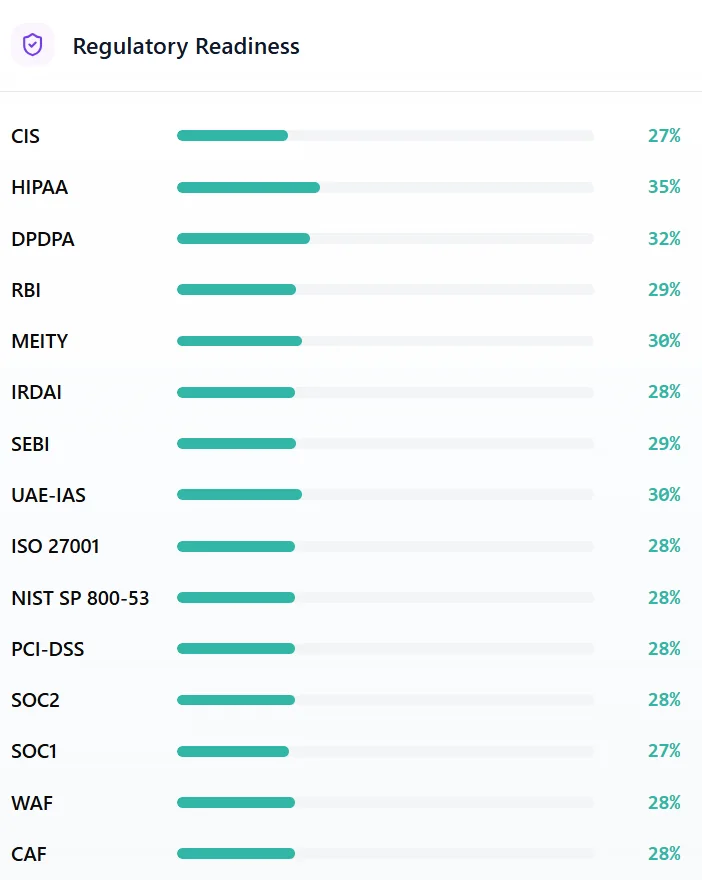
20+ frameworks, checked continuously
Codly maps each framework to testable controls, evaluates every account against them all the time, and keeps evidence per control. Indian regulators first; global standards included.
IT governance master direction, cyber security framework and payment data storage in India.
Cybersecurity and Cyber Resilience Framework for regulated entities.
Information and Cyber Security Guidelines for insurers.
Safeguards, consent and breach readiness for personal data of people in India.
Cardholder data protection, segmentation, hardening and logging.
Annex A controls tested continuously across every account.
Security, availability and confidentiality control checks.
Identify, protect, detect, respond and recover controls.
AWS, Azure, GCP, Kubernetes, Linux and Windows hardening.
Data residency and access controls for EU personal data.
Safeguards for protected health information.
Controls for regulated entities operating in the UAE.
Board policies and internal baselines as code, alongside the rest.
Framework coverage helps you meet your obligations; it does not by itself make your organisation certified or compliant. Talk to us about how controls map to your policies.
One control, many frameworks
A single check — say, encryption at rest on databases — satisfies controls in RBI, PCI DSS, ISO 27001 and SOC 2 at once. Fix it once and the evidence counts everywhere.
- Controls versioned like code
- Custom controls for internal policy
- Evidence exported per framework
See where your cloud stands in 48 hours
Connect one account with read-only access. We return a compliance-gap and savings report, then walk your team through it — free, no obligation.