Compliance that runs every minute, not once a year
Codly turns RBI, SEBI, IRDAI, ISO 27001, PCI DSS and CIS controls into policy that is checked on every resource, all the time. Drift is fixed within your rules and evidence is collected as it happens.

Point-in-time audits miss what changed yesterday.
Compliance drifts the moment an engineer ships a change. Screenshots and spreadsheets can't keep up, so audits become a scramble and risk hides between reviews. Codly encodes your obligations as policy, evaluates every account continuously, remediates misconfigurations automatically or with approval, and keeps immutable evidence for every control — so an audit is a report you export, not a project you staff.
What Compliance Management does
Compliance as code
Controls for RBI, SEBI, IRDAI, ISO 27001, PCI DSS, NIST, CIS and GDPR, versioned like software.
Continuous posture
One health, risk and compliance view across every account and cloud.
Autonomous remediation
Drift and misconfigurations prioritised and fixed within policy.
Automated evidence
Audit-ready evidence and immutable trails, generated as controls are tested.
Custom frameworks
Bring internal standards and board policies alongside the built-in ones.
Data residency
Localisation guardrails that keep regulated data in-country.
From a scramble to a dashboard
Codly continuously audits your infrastructure against leading benchmarks, resolves misconfigurations before they become findings, and keeps an evidence trail your auditors can trust.
- Controls mapped to RBI, SEBI CSCRF, IRDAI and ISO 27001
- Continuous drift detection with governed fixes
- One-click evidence packs per framework
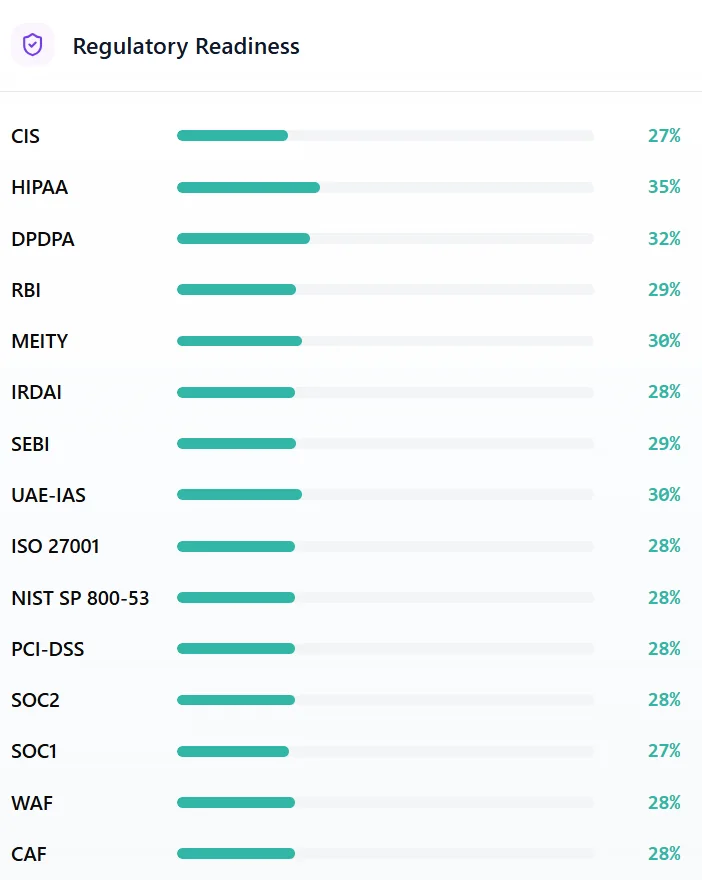
Risk you can see and rank
Instead of a different console per provider, Codly gives one prioritised view of risk across AWS, Azure, GCP and Kubernetes — so the team fixes what matters most first.
- Unified risk score across every account
- Prioritised by exploitability and blast radius
- Trend lines that prove improvement to the board
Illustrative data
Four steps, always under your policy
Map
Translate each framework into concrete, testable controls.
Assess
Evaluate every account against those controls in real time.
Remediate
Fix drift within policy — automatically or with approval.
Evidence
Collect immutable proof for every control, ready to export.
Related modules
See where your cloud stands in 48 hours
Connect one account with read-only access. We return a compliance-gap and savings report, then walk your team through it — free, no obligation.