 The agentic Cloud OS
Your entire cloud, run by AI agents — under your control.
Codly is the agentic operating system for cloud management. Specialised agents deploy, operate, secure, optimise and keep AWS, Azure, GCP and Kubernetes compliant — from one control plane, with a human approving what matters.

One operating system for everything your cloud team does
Nine modules share one kernel: one inventory, one policy engine, one agent framework and one audit trail. Start with the module that hurts most — add the rest when you are ready.
AIOps
Autonomous detection and remediation
Watch & learnFinOps
AI cost optimisation and chargeback
Watch & learnCompliance Management
Compliance-as-code across 20+ frameworks
Watch & learnCloud Atlas
Live cloud topology with security overlay
Watch & learnInventory Management
One live graph of every cloud asset
Watch & learnService Management
Agentic ITSM, incidents and change
Watch & learnOS & DB Management
CIS hardening, patching and DB tuning
Watch & learnPolicy-as-Code
Govern agents and workflows as code
Learn moreLog Analytics
Unified logs with AI investigation
Learn moreYour cloud runs on a dozen tools — and nobody owns the whole
Provisioning in one place, monitoring in another, FinOps in a spreadsheet, compliance in a ticket queue. Scripts automate tasks; nothing runs the whole. Codly replaces the sprawl with one agentic operating system.
“Our best engineers are stuck on toil.”
Scripts automate tasks, but alerts, patching and fixes still wait for a human to pick them up.
“Nobody can explain the cloud bill.”
Shared accounts and Savings Plans make chargeback guesswork, and waste hides between monthly reviews.
“Audit prep eats a quarter every year.”
Evidence is screenshotted by hand from many consoles, and drift reappears the week after the audit.
What happens when agents run your cloud
Three outcomes teams see first — each module works on its own and shares one policy engine and audit trail with the rest.
Incidents fixed in minutes — humans approve what matters
AIOps agents correlate alerts into one incident, draft a fix with its blast radius and run it. Low-risk actions run automatically; sensitive ones wait for approval in Slack, Teams or the console.
- Alert storms collapsed into explainable incidents
- Per-environment risk thresholds
- Immutable record of every action and approval
Illustrative data
Waste removed continuously — and every rupee attributed
Agents rightsize, schedule and clean up as policy. Anomalies are explained before they hit the invoice, and shared Savings Plan costs are split fairly across the businesses that use them.
- Rightsizing, idle scheduling and cleanup
- Anomaly detection with root cause
- Showback and chargeback by team or tag


Every control checked every day — evidence ready
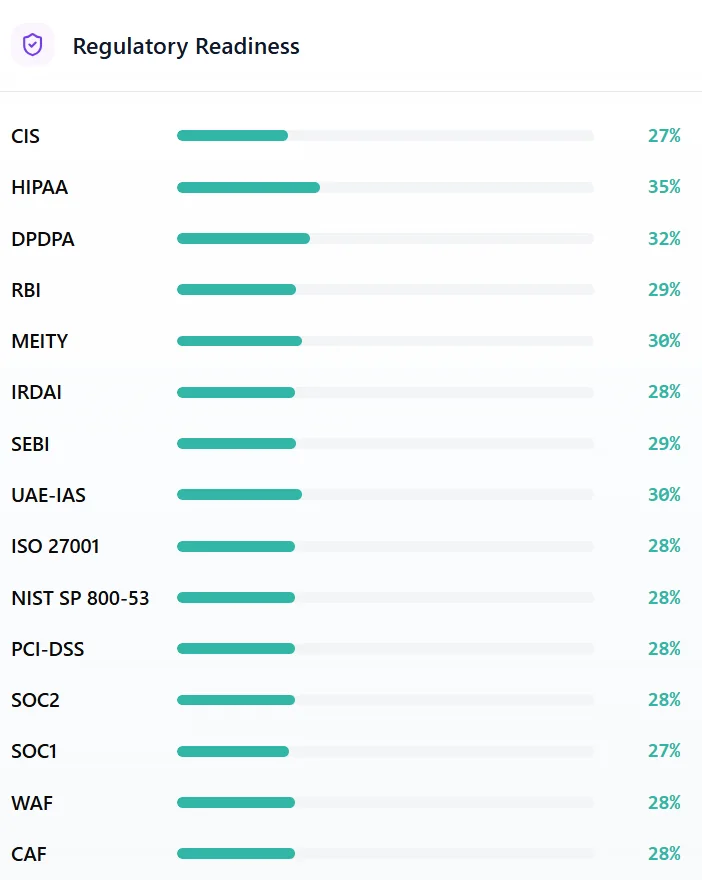
RBI, SEBI CSCRF, IRDAI, ISO 27001, PCI DSS and CIS controls run as code against every account. Drift is fixed within policy and evidence is collected as it happens.
- 20+ frameworks out of the box, plus your own
- Governed auto-remediation with approvals
- Data-residency guardrails for Indian regions
Codly doesn't just alert — it acts, under your rules
Every agent follows the same four-step loop. You decide where the human approval sits.
Observe
Streams state, cost, security posture and compliance across every account.
Plan
Reasons over context and drafts a safe, explainable runbook with its blast radius.
Approve
Risky actions pause for a named approver — in the console, Slack or Teams.
Act & verify
Executes, confirms the outcome and writes immutable audit evidence.
RBI, SEBI and IRDAI controls — not an afterthought
Global tools start with SOC 2. Codly starts with the regulators and laws you answer to in India, then covers the global standards too.
IT governance master direction, cyber security framework and payment data storage in India.
Cybersecurity and Cyber Resilience Framework for regulated entities.
Information and Cyber Security Guidelines for insurers.
Safeguards, consent and breach readiness for personal data of people in India.
Cardholder data protection, segmentation, hardening and logging.
Annex A controls tested continuously across every account.
Security, availability and confidentiality control checks.
Identify, protect, detect, respond and recover controls.
Made for financial services
Banking, NBFC & Capital Markets
RBI, SEBI CSCRF and data localisation
- Controls mapped to RBI and SEBI expectations
- Region guardrails for ap-south-1 / Azure Central India
- Private or air-gapped deployment
Insurance
IRDAI cyber security guidelines
- IRDAI-aligned control mapping
- Hybrid coverage: AWS, Azure, GCP, VMware, OpenShift
- Least-privilege and access reviews
FinTech
PCI DSS, RBI payment and lending rules
- PCI DSS cardholder-environment monitoring
- FinOps guardrails from day one
- Evidence for partner-bank reviews
Managed service provider? Run every client from one control plane
Shape Codly with us — and get priority onboarding
We're onboarding a small group of regulated enterprises as design partners. Partners get a dedicated engineer, hands-on onboarding and a direct line into the roadmap.
Your data stays inside your boundary
Codly is built for the security review it will face at a bank. Run it as a managed service in Indian regions, inside your own VPC, or fully air-gapped.
- Private or air-gappedDeploy in your VPC or on-premises.
- Data residencyData stays in the regions you choose.
- Least privilegeRead-only by default; RBAC and SSO.
- Human in the loopApproval gates on risky actions.
- Immutable audit trailEvery plan, approval and action logged.
- Your choice of AIAzure OpenAI, OpenAI, Gemini — or private.
Information security management system independently certified.
Independent VAPT by a CERT-In empanelled auditor. Summary report available under NDA.
Procure through your existing AWS billing and agreements.
Questions buyers ask us
What is an agentic Cloud OS?
A single platform that runs your cloud end to end, instead of a collection of point tools and scripts. Codly keeps one live inventory, one policy engine and one audit trail, and specialised AI agents — for operations, cost, compliance, service management, OS and databases — act on them under your approval rules.
What exactly does the free 48-hour assessment include?
You connect one cloud account with a read-only role. Within 48 hours we share a report covering compliance gaps against the frameworks you choose (for example RBI, SEBI CSCRF or ISO 27001), your top security risks and an estimate of avoidable spend — then walk your team through it. There is no cost and no obligation.
What access does Codly need?
Read-only access is enough to discover resources and assess posture and cost. Remediation permissions are optional, scoped by you, and every action is still governed by policy and approvals.
Can Codly run inside our own environment?
Yes. Codly can run as a managed service in the regions you choose, inside your own VPC, or fully private and air-gapped for regulated workloads.
Do we need to replace our existing tools?
No. Codly sits above your stack and works with what you already run — Terraform, Kubernetes, ServiceNow, Jira, Freshservice, Slack, Teams and your SIEM.
How do approvals work?
You set risk thresholds per environment. Low-risk actions run automatically; sensitive changes pause for a named approver in the console, Slack or Teams, with the plan and blast radius shown first.
How is Codly priced?
Plans bundle modules and are priced on your cloud footprint and number of accounts. You can also buy through AWS Marketplace. Most teams start with the free assessment, which gives us what we need to quote.
See where your cloud stands in 48 hours
Connect one account with read-only access. We return a compliance-gap and savings report, then walk your team through it — free, no obligation.